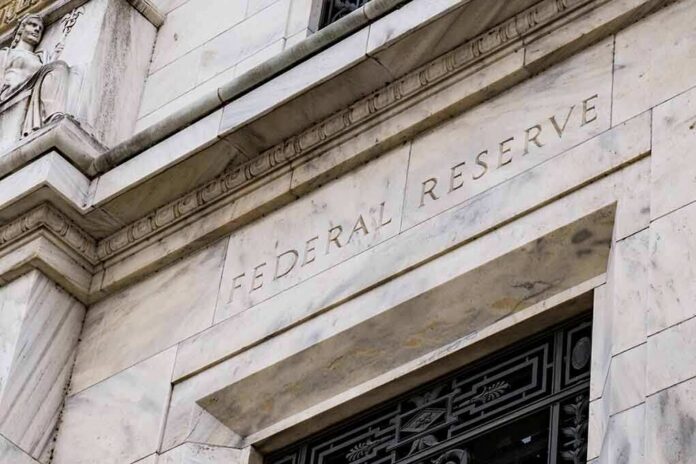
Two hundred seventy-nine security alarms screamed, and the central bank still could not say what walked out the door.
Story Snapshot
- A Federal Reserve watchdog found major gaps in offboarding security controls.
- A retiring staffer triggered 279 data-loss alerts in 90 days; 111 flagged possible rate-policy files.
- The Office of Inspector General said weak follow-up left the facts unclear.
- The Board agreed to fix insider-risk and offboarding processes, the watchdog said.
The Alert That Wouldn’t End
The Federal Reserve’s Office of Inspector General reported that a departing employee set off 279 data-loss prevention alerts in the last three months before retiring in July 2024. The tool flagged 111 of those alerts as possibly involving Federal Open Market Committee classified material, the most sensitive kind of interest rate information. The watchdog said the Board had gaps in spotting and handling removals of information by departing staff. That is not a paperwork slip. That is a control breakdown.
The inspector general learned about the situation in July 2025, a year after the employee left, during an audit of offboarding controls, which raised the stakes further. Officials could not confirm exactly what left, because the process to log, escalate, and preserve evidence did not work as designed. The watchdog issued a “management alert,” a formal warning that demands quick fixes. It also tied this case to wider insider-risk weaknesses the Board must address.
Why This Matters To Markets And Taxpayers
The Federal Open Market Committee steers the price of money. Files about rate moves, balance sheet plans, or staff forecasts can move trillions. If even the hint of that data can leave without a clean trail, the risk is not abstract. The inspector general did not state a final misconduct finding. But the office did say the alert storm helped expose systemic problems with offboarding, evidence handling, and response coordination across teams. That means the next case could be worse if the fixes lag.
Readers who manage businesses know the pattern. Data-loss tools catch a lot and cry wolf often. False alarms happen. But 279 alerts in 90 days should force fast triage, tight logs, and decisive action. The Board’s own watchdog said that did not happen. That aligns with common sense and with conservative priorities: guard the crown jewels, verify access, and maintain clear chains of accountability. Culture follows process. If process is fuzzy, culture drifts, and risk grows.
What The Fed Says It Will Do Now
The Board agreed with recommendations to tighten offboarding. The commitments include better training on data rules, faster escalation for policy violations, and stronger tracking when staff return devices and credentials. The plan also targets insider-risk governance, which the inspector general flagged in a separate report as needing more rigor. Those moves are necessary. Yet they will only matter if managers test them under stress and document every step. Paper promises will not stop the next flash drive.
The inspector general’s work plan shows this is not a one-off concern. Ongoing reviews focus on records management, security debriefs, and the shutdown of identity cards at exit. That list points to a full life-cycle approach: grant the least access needed, watch for odd movement, and shut doors fast when people leave. Private firms solved this by pairing data-loss tools with human threat teams who act in hours, not months. The Board’s path should look the same.
The Conservative Read: Controls, Consequences, Confidence
Public trust rides on competence. Central banks manage secrets that swing mortgage rates and savings. When alarms blare and no one can say what left, confidence takes a hit that headlines alone cannot fix. The fix is not a press release. The fix is discipline. Build logs that stand up in court. Cut access on notice of departure. Record every transfer. Reward fast reporting. Penalize slow follow-up. Do that, and both markets and taxpayers get what they deserve: stewardship, not shrugging.
What To Watch Next
Watch for concrete milestones: new insider-risk playbooks, tabletop drills, and metrics on alert response times. Look for fewer alerts, but faster closure with better evidence. Expect clearer lines between the data-loss team, human resources, and legal. The inspector general put the Board on notice. The next audit will show if the culture changed. In the meantime, the lesson travels well: you cannot protect what you do not track, and you cannot track what you do not train people to handle.
Sources:
americanbanker.com, thedeepdive.ca, thecompanychronicle.com, bankingdive.com, yahoo.com, oig.federalreserve.gov, cdn.govexec.com
© restoreamericanglory.com 2026. All rights reserved.